Encrypted per field,
wherever it runs.
The keys can stay with you, so only the parties you choose can open a field. It runs on your premises, in your own cloud or hosted by us.
Trusted by government and industry
What keeps the data protected.
Cryptography decides who can open what, so access does not depend on our promises.
01
Deployment where you choose
The connector runs next to your systems, on your premises or in your own cloud account, and the rest of the layer can run there too or be hosted by us.
02
A key per field
With the connector next to your systems, each field is encrypted with its own key before it leaves your environment. When the keys stay with you too, a breach at mintBlue exposes only encrypted data.
03
Access per field and per party
Each recipient gets keys only for the fields it is entitled to, so a partner, an auditor and a supervisor can each see a different part of the same record. Access is tiered, from seeing that an exchange happened to opening its content.
04
No lock-in
The protocol is open and your data stays retrievable, so leaving does not depend on our cooperation. The layer does not depend on a particular cloud provider either.
From policy to proof
Most platforms enforce permissions in application code, so one vulnerability can expose everything. Cloud services ask you to trust the vendor with your data, consortium networks tie you to one set of members, and self-hosting means building it all yourself.
Here, access follows the keys, wherever the layer runs.
Policy-based security
- Application-layer access control
- Vendor has access to encryption keys
- Trust depends on contractual promises
- Platform compromise exposes all data
Proof-based security
- Cryptographic access control
- Encryption at the source, with keys that can stay with you
- Access enforced by encryption keys
- Without your keys, a breach exposes only encrypted data
How your data stays yours
How a field is protected
From master key to encrypted field. With the connector next to your systems and the keys with you, our infrastructure only handles encrypted data.
- 01
Keys from your master key
Each field's key is derived from a master key held where you choose, such as a passphrase.
- 02
Derived, never sent
When you hold the keys, they are derived on your side and never sent over the network.
- 03
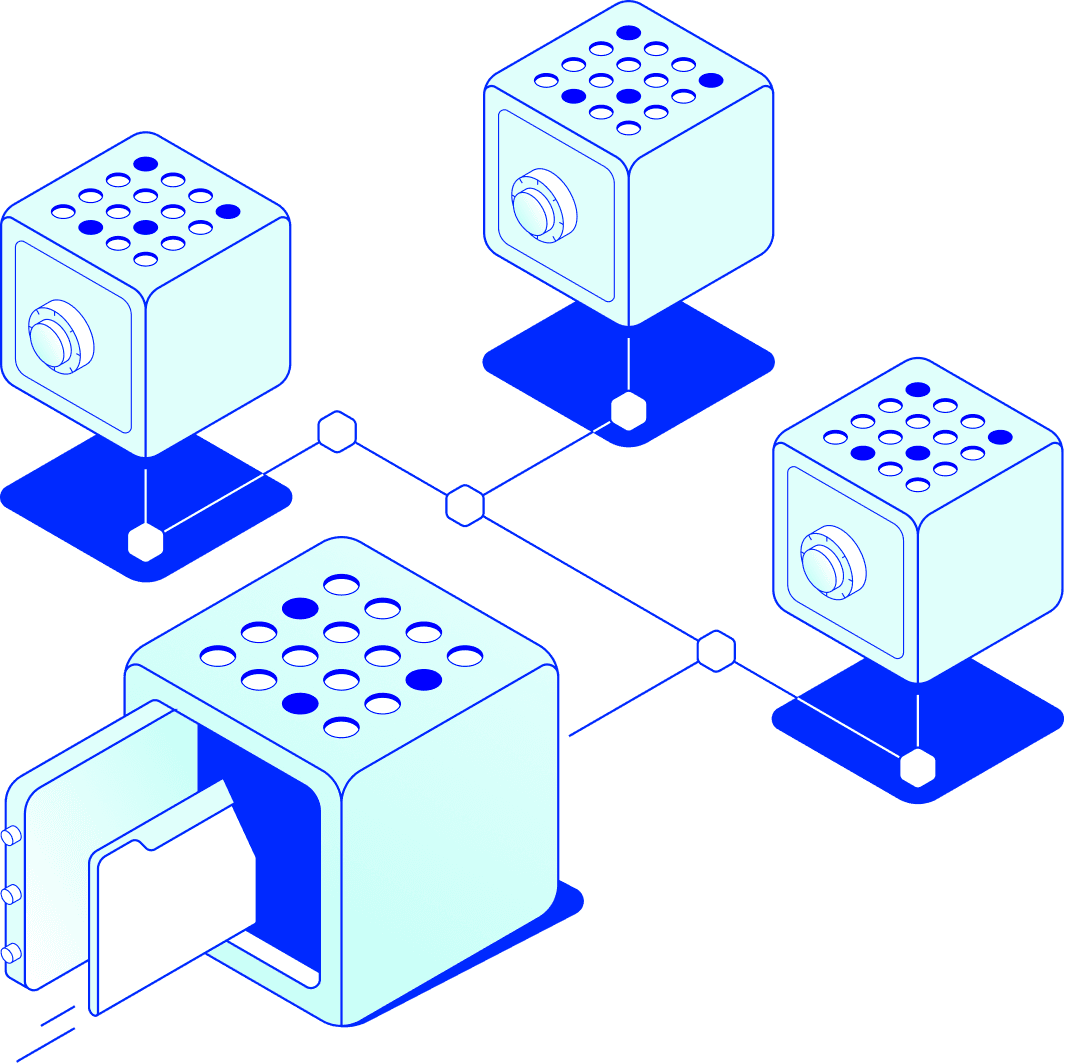
Encrypted before sending
Each field is encrypted with its own key before the connector sends it. Authenticated encryption (AEAD) shows whether anything was altered on the way.
- 04
Opened only with the right key
Only parties holding the right keys can decrypt a field, and you decide per partner which fields that is. A withdrawn mandate stops future requests.
Run it where you choose.
Three ways to deploy, with the same encryption and the same audit trail.
Built for audits and supervision.
Every exchange is signed, checked against its mandate and recorded in a tamper-evident audit trail. An auditor or supervisor can verify it without receiving copies of your data.
Encryption per field and selective disclosure support data minimisation under the GDPR, and you decide where the data is stored. mintBlue is a European company under European jurisdiction.
Under European law
Frequently asked questions
Data protection
Architecture
Next step
Put it through your security review.
Bring your requirements for deployment, keys and access. We walk your security team through the architecture and the set-up that fits them.
Next step
Put it through your security review.
Bring your requirements for deployment, keys and access. We walk your security team through the architecture and the set-up that fits them.